
Cyber Defense for Power & Energy
Turn grid telemetry into investigated cases, evidence-backed records, and stronger detections. Operators verify every action.
Partners & Programs
The threats electric utilities face now.
Third-party access crosses critical boundaries.
Vendors, integrators, and remote maintenance create trusted paths that still need visibility and evidence.
Distributed assets widen visibility gaps.
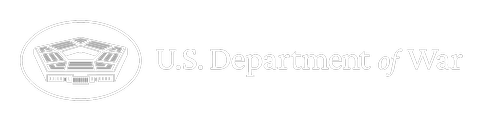
Control centers, substations, field networks, and engineering systems spread activity across a large operating footprint.
Operational disruption raises the stakes.
When malicious activity reaches grid operations, the incident can quickly become a reliability problem.
Every capability. One platform.
Threat detection, investigation, reporting, and approved IT validation across connected, on-premises, and air-gapped grid environments.
Network Detection and Response
Passively surface suspicious network activity across control centers, substations, and engineering workstations.
Explore NDRAlert Investigation
Turn connected alerts into evidence-backed cases ready for operator review.
Explore Alert InvestigationThreat Hunting
Hunt across monitored utility networks. Findings arrive with evidence.
Explore Threat HuntingHost and Network Forensics
Reconstruct what happened from the traffic and preserve the record.
Explore ForensicsCampaign Intelligence
Related cases become one attributed campaign assessment.
Explore Campaign IntelligenceIncident Reporting
Turn investigated cases into structured incident reports.
Explore Incident ReportingAgentic Penetration Testing
Validate approved IT paths and retest the fix. Never used for OT penetration testing.
Explore Pen TestingSee it on your grid traffic.
Bring what you already run. See the path from signal to verified response.
What the investigation produces.
-
Investigated cases
What happened, affected systems, and supporting evidence.
-
Campaign context
Related activity organized into an environment-level assessment.
-
Incident reports
Structured reports generated from investigated cases and supporting evidence.
-
Recommended next steps
Response and remediation actions presented for operator review.
faster from detection to response inside the CrunchAtlas workflow, based on internal testing.
Power and energy resources.
Guidance on internal network monitoring, supply chain risk, and third-party access for electric utilities.
NERC CIP-015
What the INSM requirement covers, when it takes effect, and the monitoring and evidence workflow utilities need to support.
Explore CIP-015NERC CIP-013
What the supply chain risk standard requires for vendor incidents, remote access, access termination, and product risk.
Explore CIP-013Third-Party ICS Access
Trace vendor access from the remote entry point to the operational systems, privileges, and evidence it can reach.
Review Third-Party AccessPower and energy questions, answered.
What do we actually get for CIP-015?
Get internal visibility, investigated cases, preserved evidence, and clear reports. CrunchAtlas supports CIP-015 INSM workflows. You own compliance.
Does anything touch our operational devices?
No. AtlasCyber reads copied traffic and existing tool output. Nothing installs on or commands relays, PLCs, or HMIs.
We've a SIEM and OT monitoring already. Where does this fit?
Your tools detect. AtlasCyber correlates the evidence, investigates the case, maps the technique, and returns a verdict and next step.
What can an auditor look at?
Every case keeps its evidence, timeline, affected assets, mapped techniques, verdict, and next step. Reports come from that record.
Can the whole thing run air-gapped?
Yes. AtlasCyber can run fully on premises or air-gapped, with investigation local to the environment.