 CrunchAtlas

Agentic Security for Critical Operations.
Continuous threat investigation helps operators stay ahead of attacks and keep critical systems running.
Trusted partners
The threat moved inside the plant.
From the wire to a verdict.
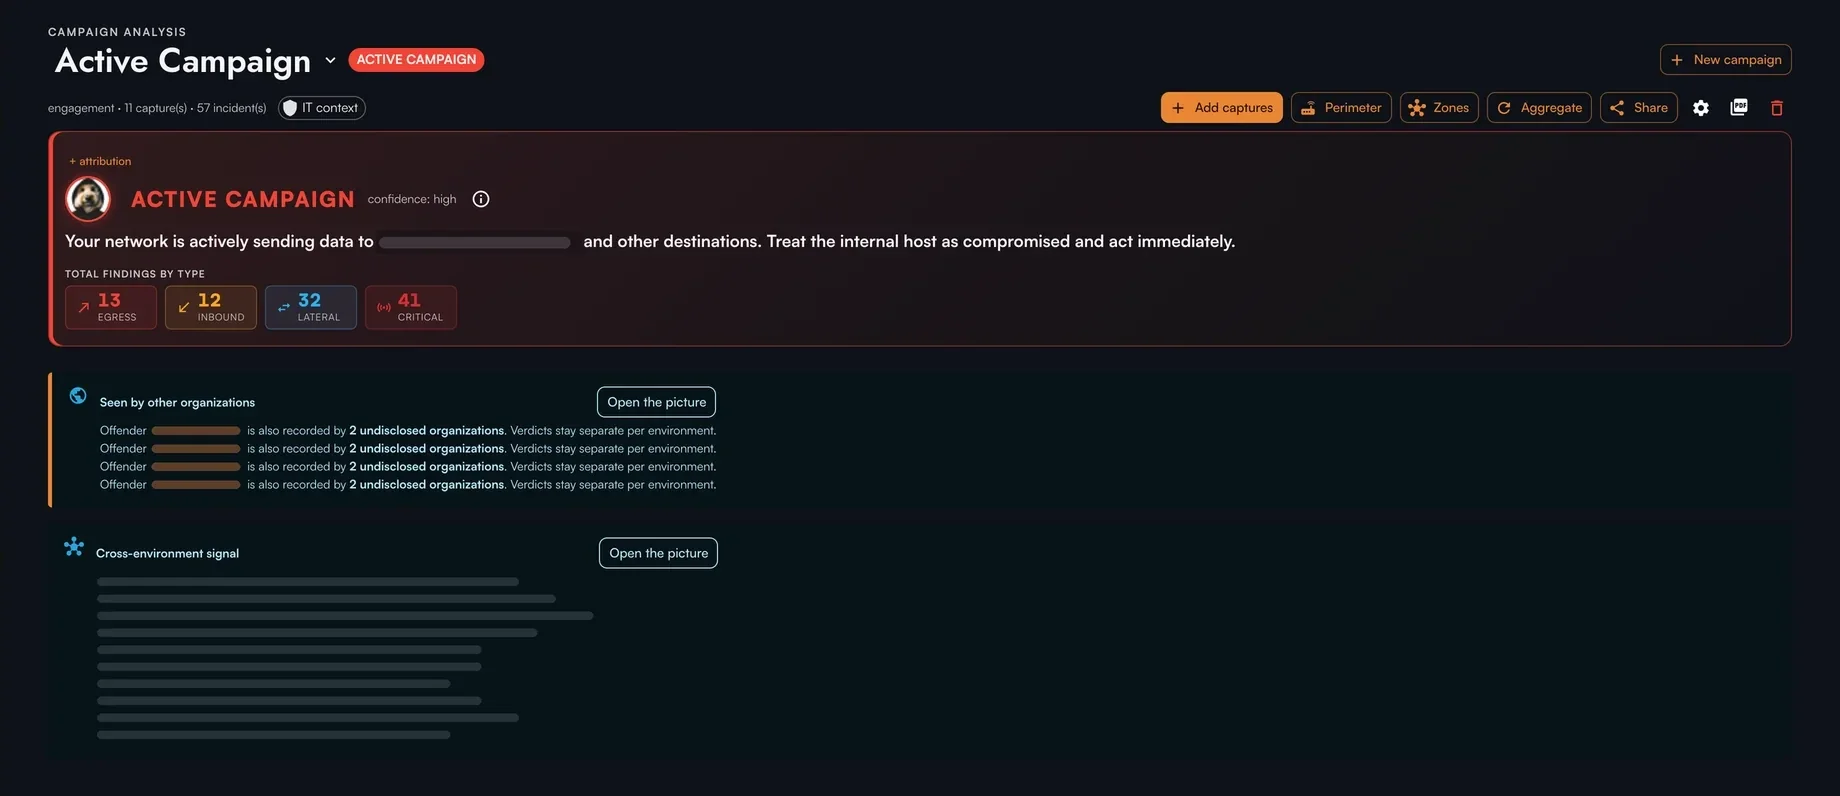
From detection to a documented investigation.
Evidence for and against, what was ruled out, and what to do first.
Passive. Touches nothing.
AtlasCyber analyzes a passive copy of network traffic without installing software on industrial controllers or sending them commands.
A verdict you can check.
Real or benign, how sure, and the evidence behind it.
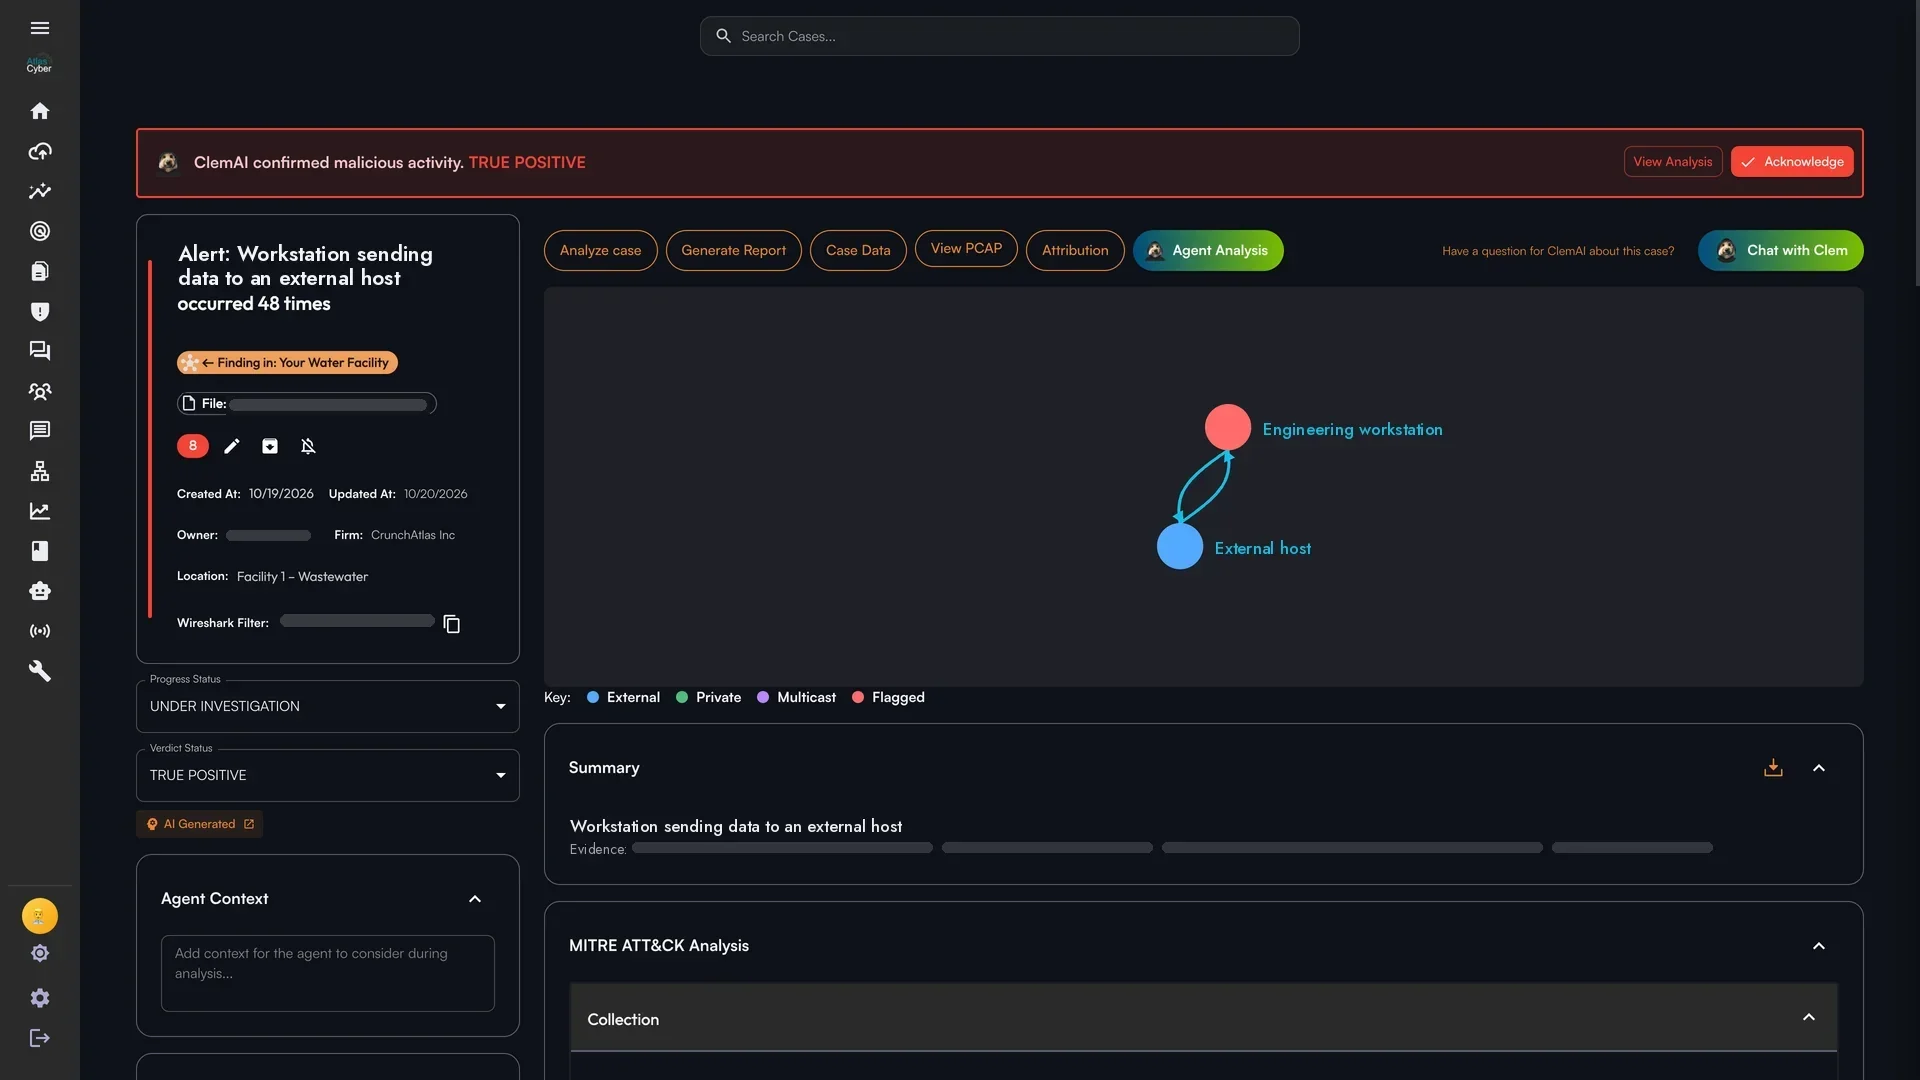
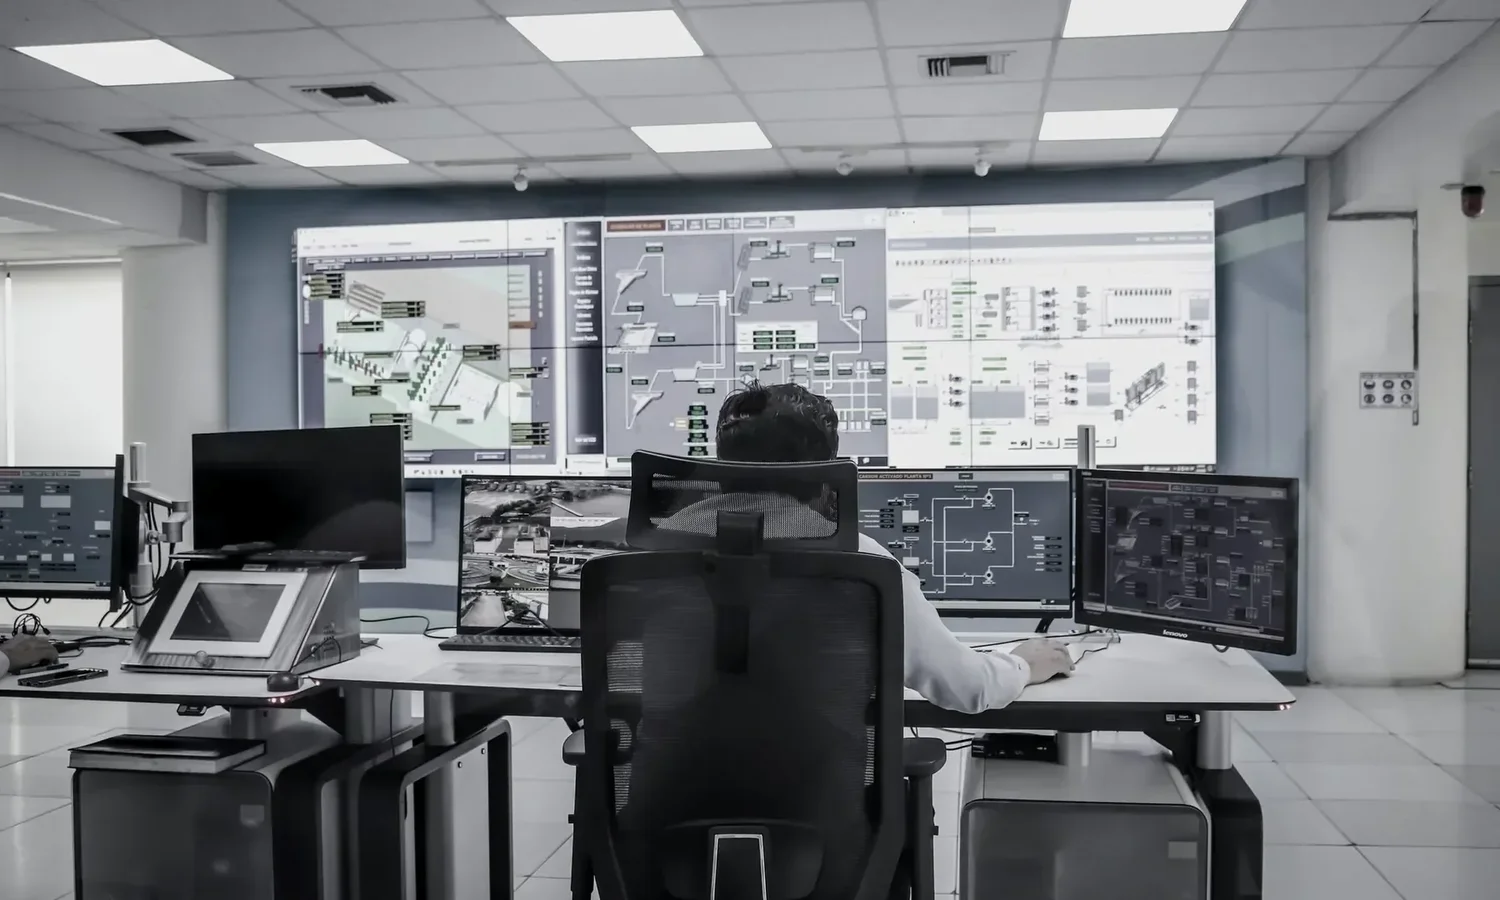
The investigation is already underway.
ClemAI assembles the evidence, identifies related activity, and prepares findings for your team to review.
See how it fits your environment.
IT, OT, and ICS, hosted, on-site, or air-gapped.
Detection, investigation, and validation in one platform.
Built for infrastructure that can't go down.
Runs where your network does.
Enterprise
Centralized investigation across the sites and network connections approved for centralized visibility.
Hosted
We run it. Your sensor sends an encrypted, outbound-only feed.
On-site
It runs on hardware in your facility. Your data stays there.
Built by operators
45+
years in Army special operations, cyber, and intelligence.
 Founded by Ben Faberlle, CEO, and Sean McQuade, COO.
See why teams trust us to defend their environment.
See how AtlasCyber and ClemAI detect threats, investigate activity, hunt for adversaries, and document findings across IT, OT, and ICS.
Talk to our teamSign up for our newsletter